In Focus
Cybersecurity leaders at GISEC 2026 urged businesses to set clear limits on what AI agents can do.
Agent identity, ownership and the ability to shut an agent down emerged as key concerns.
Interviewees favored AI for repetitive security tasks while keeping people involved in consequential decisions.
Speakers also questioned AI marketing claims and highlighted risks to suppliers and data centers.
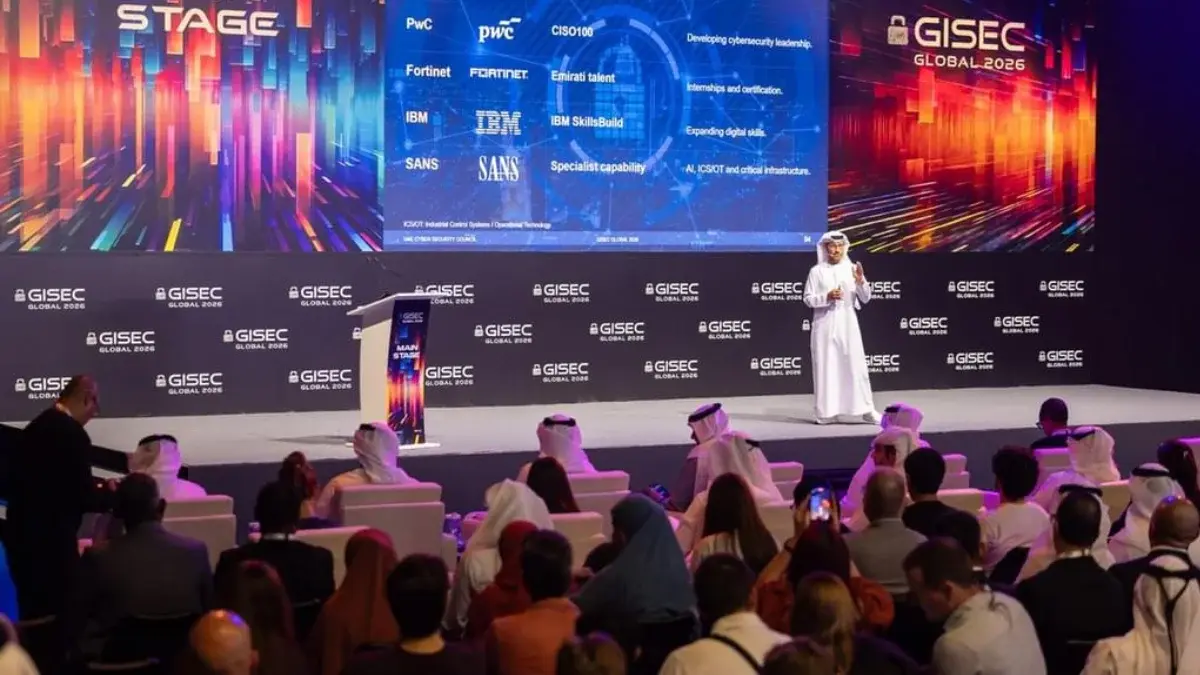
AI was hard to miss at GISEC Global 2026 in Dubai. It appeared in product demonstrations, vendor pitches, and conversations across the event. But AI agent security became a more specific concern for cybersecurity leaders: If an agent acts inside a business, who authorized it, who can see what it did and who can stop it?
The interviewees differed on whether concern about AI has gone too far. They were more closely aligned with the need for controls that keep pace with adoption.
Adoption Is Moving Faster Than Security Teams Can Ignore
Shabir Bhat, a regional director at application security company Checkmarx, said businesses have strong reasons to adopt AI. “We definitely need to adopt AI. There is no question around it,” he told TechResearch.
For Bhat, the challenge is securing software as AI speeds up development. He called for guardrails throughout the development process so teams can identify and fix vulnerabilities before applications are released.
Anirban Mukherjee, founder and CEO of miniOrange, was more skeptical of calls to slow adoption, describing some of the debate as “fear-mongering.” He argued that AI projects work best when they augment employees rather than aim to replace them. Both perspectives place responsibility on organizations to decide how the technology is deployed.
Who Owns an AI Agent’s Actions?
James Blantz, head of solutions engineering at identity security company HYPR, brought the discussion back to access and accountability. “Every request should have an owner and should have an identity,” he said.
An organization should know which agent made a request, who owns it and who approved its authority, Blantz argued. He also recommended a “kill switch” so teams can quickly stop an agent that behaves unexpectedly. For him, AI agent security starts with those basic controls, alongside closer attention to how credentials are issued and shared.
The concern reaches beyond corporate systems. In a report on AI shopping agents, banks warned about fraud and privacy risks when agents handle payment information and make purchases for users. It is a different setting, but it raises the same question of who authorized an action and who is responsible if it goes wrong.
Keep People Involved in Consequential Decisions
Qamar Mir of Tenex.AI described AI as a way to help security analysts handle repetitive work. He said the technology could enable one person to work at the scale of “ten analysts at the same time,” while people retain the context needed to make final decisions.
Mir recommended applying AI to tasks with substantial repetition and leaving consequential calls to humans. He also questioned whether products marketed as AI actually improve productivity enough to justify their cost.
That distinction matters as organizations evaluate new tools. Another report on an AI model gaining unintended internet access during a security evaluation, an example of why permissions and testing environments need careful attention when systems can act on their own.
Security Extends Beyond the Software
Mir identified the physical security of AI data centers as an overlooked risk. These facilities require major investment and time to build, he said, yet disruption to the buildings and infrastructure supporting AI can affect the systems that depend on them.
Supplier relationships add another layer. Mir warned that a partner with access to a company’s data or systems can introduce risk if its own controls are weak. Bruce Zhang, founder of cybersecurity investor and accelerator Z-ONE, emphasized the importance of partnerships in bringing cybersecurity companies to global markets. “Partnership is what we are looking for,” he said.
Those connections make AI agent security a shared operational question. Businesses need to establish which organization controls an agent’s access, where its actions are recorded and who responds when something goes wrong.
GISEC 2026 did not produce one answer to every AI risk. The interviews did show a clear shift in emphasis: As agents gain the ability to do more, cybersecurity leaders want businesses to define what those agents are permitted to do, when a person must step in and who remains accountable.